Showing posts with label ABK. Show all posts

Tuesday, September 13, 2011

Open Intelligence Gathering FOR Passive Reconnaissance FROM "Eden Guide To Hacking"


Open Intelligence Gathering : github.com/abhishekkr.....Open_Intelligence..
FOR 
FROM 
The following content structure is discussed in detail @
https://github.com/abhishekkr/eden_guide_to_hacking/blob/b00ef1502b9f91953f5d734efd4a03c3a0f04002/part1_Hacking_Cycle/chapter4_Reconnaissance/section0_Passive_Recon/article0_Open_Intelligence_Gathering.txt

~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~[+] Open Intelligence Gathering
 |
 |[+] What Is Open Intelligence?
 |
 |[+] Legal Documents Got Them
 |
 |[+] Search Engines Sort Them
 |
 |[+] Web Activity Caught Them
 | |
 | |[+] You Blog/Comment
 | |[+] You Socialize
 | |[+] You Subscribe
 | |[+] You Show/Click Ads
 | |[+] Even If You Surf Web
 | |_
 |
 |[+] Automating the Act
 | |
 | |[+] Paterva Maltego CE
 | | |[+] URL
 | | |[+] What it does?
 | | |[+] Example Usage
 | | |_
 | |
 | |[+] The Harvester
 | | |[+] URL
 | | |[+] What it does?
 | | |[+] Example Usage
 | | |_
 | |_
 |_

~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~~

Wednesday, March 30, 2011

Full site SSL-ification is not an option, need to make SSL secure first

I have  heard (Recently and in past) security aware lives wasting a lot of their potential over the argument like 
+ 'Basic HTTP is insecure' {sometimes in novice past}
+ 'SSL-ify entire web service' {still a lot push is there}

Now, 'Basic HTTP' being insecure is not a flaw by design... but a flaw by choice.
First of all, when foundation of HTTP were laid attackers were not in the scene. The only concern was ultra productive usability and that is not possible putting all kind of security checks on the service.
Secondly, HTTP wasn't meant to be secure, it was just meant to transfer data in adhering to a protocol which can be used by web-services to recieve user's requests and deliver requested content, that's all.
Cryptography mixed into it will destroy the ease and speed it has. Cryptography over it is instead a necessary (in some cases) and correct (design) option.
Though it has been haunting the websites by attacks like
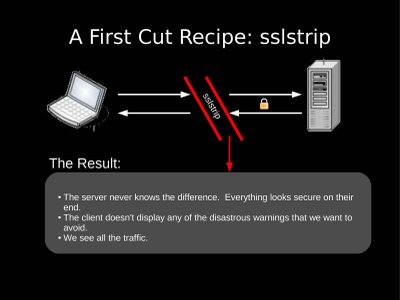
+[] SSL Stripping
It's due to a flaw in the way Security is implemented in a web application. For example, you visit Facebook Login page at facebook.com which have a HTTPS link in its unprotected page-content to send over the credentials in a protected manner. But what if some attacker using Monkey-in-the-Middle strategy changed that HTTPS link to a HTTP link and sniff your sent credentials... w00t right.
+[] Sidejacking
It occurs due to web-application sending cookie information over non-ssl links. This allows any Man-in-the-Middle to sniff the cookie then replicate in his/her own browser and use the service identifying user just on basis of cookie information... it pwn3d services like GMail, Y!Mail, Hotmail, etc. until Q1-2010.

Then, 'Full Site SSL-ification' is a good choice from theoretical security point-of-view, but just in theory.
Different SSL-Defeating attacks involving
+[] Flaws in Libraries like NSS
There was a (earlier exploited, later) famous flaw in libraries with the case of NULL inclusion in URLs used for Domain name on which SSL Certificate is being issued. Mozilla Engine used NSS Cryptography libraries purely written in C and using basic insecure string functions for comparisons were tricked by certificates for domain name like <<www.paypal.com\0innocent.com>> stopping at first null after <<www.paypal.com>>. Webkit, Opera used null-stripping but they were tricked in just reversed attack using certificates for domain-name like <<www.pay\0pal.com>> stripping out usefull null.
+[] Fake SSL Certificate generation
Not a flaw in SSL, neither in its implementation but in the authorities enforcing it.
In a recent disclosure, Comodo Inc (a major issuer of SSL Certificate) accepted that an attacker was able to get credentials of 'Comodo Registration Authority' based in Southern Europe.
An Iranian attacker used the privilege to issue 9 fraud SSL certificates to 7 web domains including those for Google, Yahoo and Skype.


  So, if you will look deeper into serial-murder case file of
  SSL Certificates, you'll see it ain't safe... 

  and so there is no point in argument over its mixed/full
  implementation.

Monday, September 6, 2010

XSS Defeating PoC : if have any time for Experimentation


It's still in experimental state, if you find some time please try it and let me know of your experience.

Video Demo of the same PoC: http://www.youtube.com/watch?v=ENiiAccY1v0


I was working on a XSS-Patch PoC, which I now feel works proper enough to prove its point.
This neither require Web-Developers for any Filtering/Validation, nor any javascript blocking add-on on user's browser.

I'm not good at explaining still I've tried to do that in the above linked WhitePaper.

And the ZIP file can be extracted, having 'StartDemo.bat' to be executed to start the server already patched with XSS Subverting Module.
Then browse, 'http://localhost/tweet.htm' in any browser... and it lets you Submit any text to Server w/o validation which is as it is saved there. But when retrieved on 'Read...' remains inactive for any

Thursday, August 26, 2010

hrberry.com :: php flaw self-inviting DoS, leaked framework and server info [by, ABK]

Posted@ https://sites.google.com/site/abklabs/home/secured/posts.xml

[]Patched:
Yes

[]Product Name:
http://www.hrberry.com
Payroll Helpdesk, serving several prestigious companies

[]Victim Name:
Ascent Consulting Services Pvt. Ltd.
[http://ascent-online.com]

[]Vuln Summary:
There were validation flaws for GET Request Parameters sent to CAPTCHA image generating PHP script on the Portal.
This allowed attacker to trick the app to generate any number of characters consuming processing power.
It had a timout after 30 seconds (too much) and generated error message with full PATH of PHP file.
Also worked on older un-patched version of OpenSSL.

to read detailed Description... click here

Saturday, January 16, 2010

ABK SiteHoster -=[developing a HTTP Network Server to be secure at implementation]=-

ABK SiteHoster 

Sourceforge Link : http://sourceforge.net/projects/sitehoster/ 


Youtube Demo Link: http://www.youtube.com/watch?v=CogPa646vi8

Currently in it's BETA stage and can only serve URL as per HTTP v0.9, so not secure but basic WebServer

Actually developing it as a HTTP Network Server to be secure at its implementation, normally all WebServer present out there are vulnerable cuz they didn't implemented Security at their very core but as an extra sheild outside.
Here in this project I'll be aiming at making it secure from the core itself and making it self-secured by immunizing it from all kinds of Web-App attacks.


ABK SiteHoster is aLEHNS (a Lightweight Extensible HTTP Network Server). Developed in pure Java. Currently supports HTTP 0.9, easily delivering normal HTML oriented WebSites. Aiming to be a full-fledged WebSite Server with all Web Services.